AI agents are one of the most overpromised ideas in applied AI right now.
On the surface, they sound powerful. Give an agent a goal, let it think across steps, connect it to tools, and it will act like a smart digital operator. That is the dream many teams buy into.
But in practice, many AI agents do not fail because the model is too weak. They fail because the system around the model is poorly designed.
When an AI agent has vague scope, unclear authority, broad permissions, and no checkpoints, it becomes unpredictable. It may sound confident, move quickly, and still create expensive mistakes.
That is why the real challenge in agent design is not just intelligence. It is structure.
Why AI agents fail more often than people expect
A lot of AI agent demos look impressive because they operate in a controlled environment. The task is short, the inputs are clean, and the consequences of mistakes are low.
Real work is different.
In real environments, agents face incomplete context, conflicting instructions, messy tools, unclear ownership, and changing priorities. Once that happens, many systems begin to break down. Not because the idea of AI agents is useless, but because the design lacks boundaries, roles, and checkpoints.
Many teams assume that if an agent can reason, it can govern itself. That assumption is one of the main reasons AI agent projects become chaotic.
An agent without structure does not become autonomous. It becomes unstable.
The first problem: unclear boundaries create scope drift
One of the most common reasons AI agents fail is that no one clearly defines what the agent should and should not do.
This sounds simple, but it is often ignored.
Teams say things like
“Let the agent handle customer support.”
“Let the agent manage outreach.”
“Let the agent review documents.”
“Let the agent help with operations.”
These instructions are too broad. They describe a domain, not an operational boundary.
A reliable AI agent needs a defined scope. It must know
- what task category it owns
- what actions it is allowed to take
- what data it can access
- what decisions require escalation
- what outcomes count as success
- what conditions should stop execution
Without that clarity, the agent starts making assumptions. It begins answering questions outside its competence, triggering tools at the wrong time, or continuing workflows long after human review is needed.
This is not intelligence. This is scope drift.
The second problem: no clear role design
Another major reason AI agents fail is poor role design.
Many teams build one agent and expect it to do everything. Research, summarize, judge, decide, write, send, update, and monitor. That is not system design. That is role overload.
In healthy operational systems, roles are separated for a reason. The same principle applies to AI.
A research agent should not automatically be a decision agent. A drafting agent should not automatically be a publishing agent. A monitoring agent should not automatically be an execution agent.
When one agent holds too many responsibilities, errors compound faster. A weak assumption in one step becomes an action in the next step. And because the workflow feels continuous, the mistake is harder to detect.
Better AI systems are built through role discipline.
What strong role design usually looks like
A more reliable AI workflow often separates functions such as
1. Input or intake role
This role gathers the request, cleans the data, and clarifies intent.
2. Research or retrieval role
This role finds relevant information, sources, or context.
3. Analysis role
This role interprets the information and identifies possible options.
4. Drafting role
This role creates an output based on defined criteria.
5. Review or checkpoint role
This role checks for quality, policy, logic, or risk.
6. Execution role
This role performs a limited action only when conditions are met.
That design is less flashy than “one super agent.” But it is far more reliable.
The third problem: permissions are too loose
An AI agent with unrestricted access is not a sign of sophistication. It is a sign of weak governance.
Too many agent systems are given permission to search, email, edit records, trigger workflows, or call external tools with very little constraint. That creates a dangerous pattern: the system can act faster than the organization can supervise.
In many failed agent implementations, the problem is not that the output was bad. The problem is that the agent had enough permission to make the bad output consequential.
For example, an agent may
- send a message to the wrong recipient
- modify the wrong document
- update a CRM record incorrectly
- perform an action based on partial context
- continue executing after a hidden error appears upstream
This is why permission architecture matters.
A well-designed AI agent should have limited authority by default. It should operate with the smallest permission set required for its task. Any action with external consequences should pass through verification or escalation logic.
In other words, not every capable action should be an allowed action.
The fourth problem: there are no checkpoints
This is where many teams lose control.
They assume that because an agent can complete multiple steps, it should complete all of them without interruption. That assumption creates failure loops.
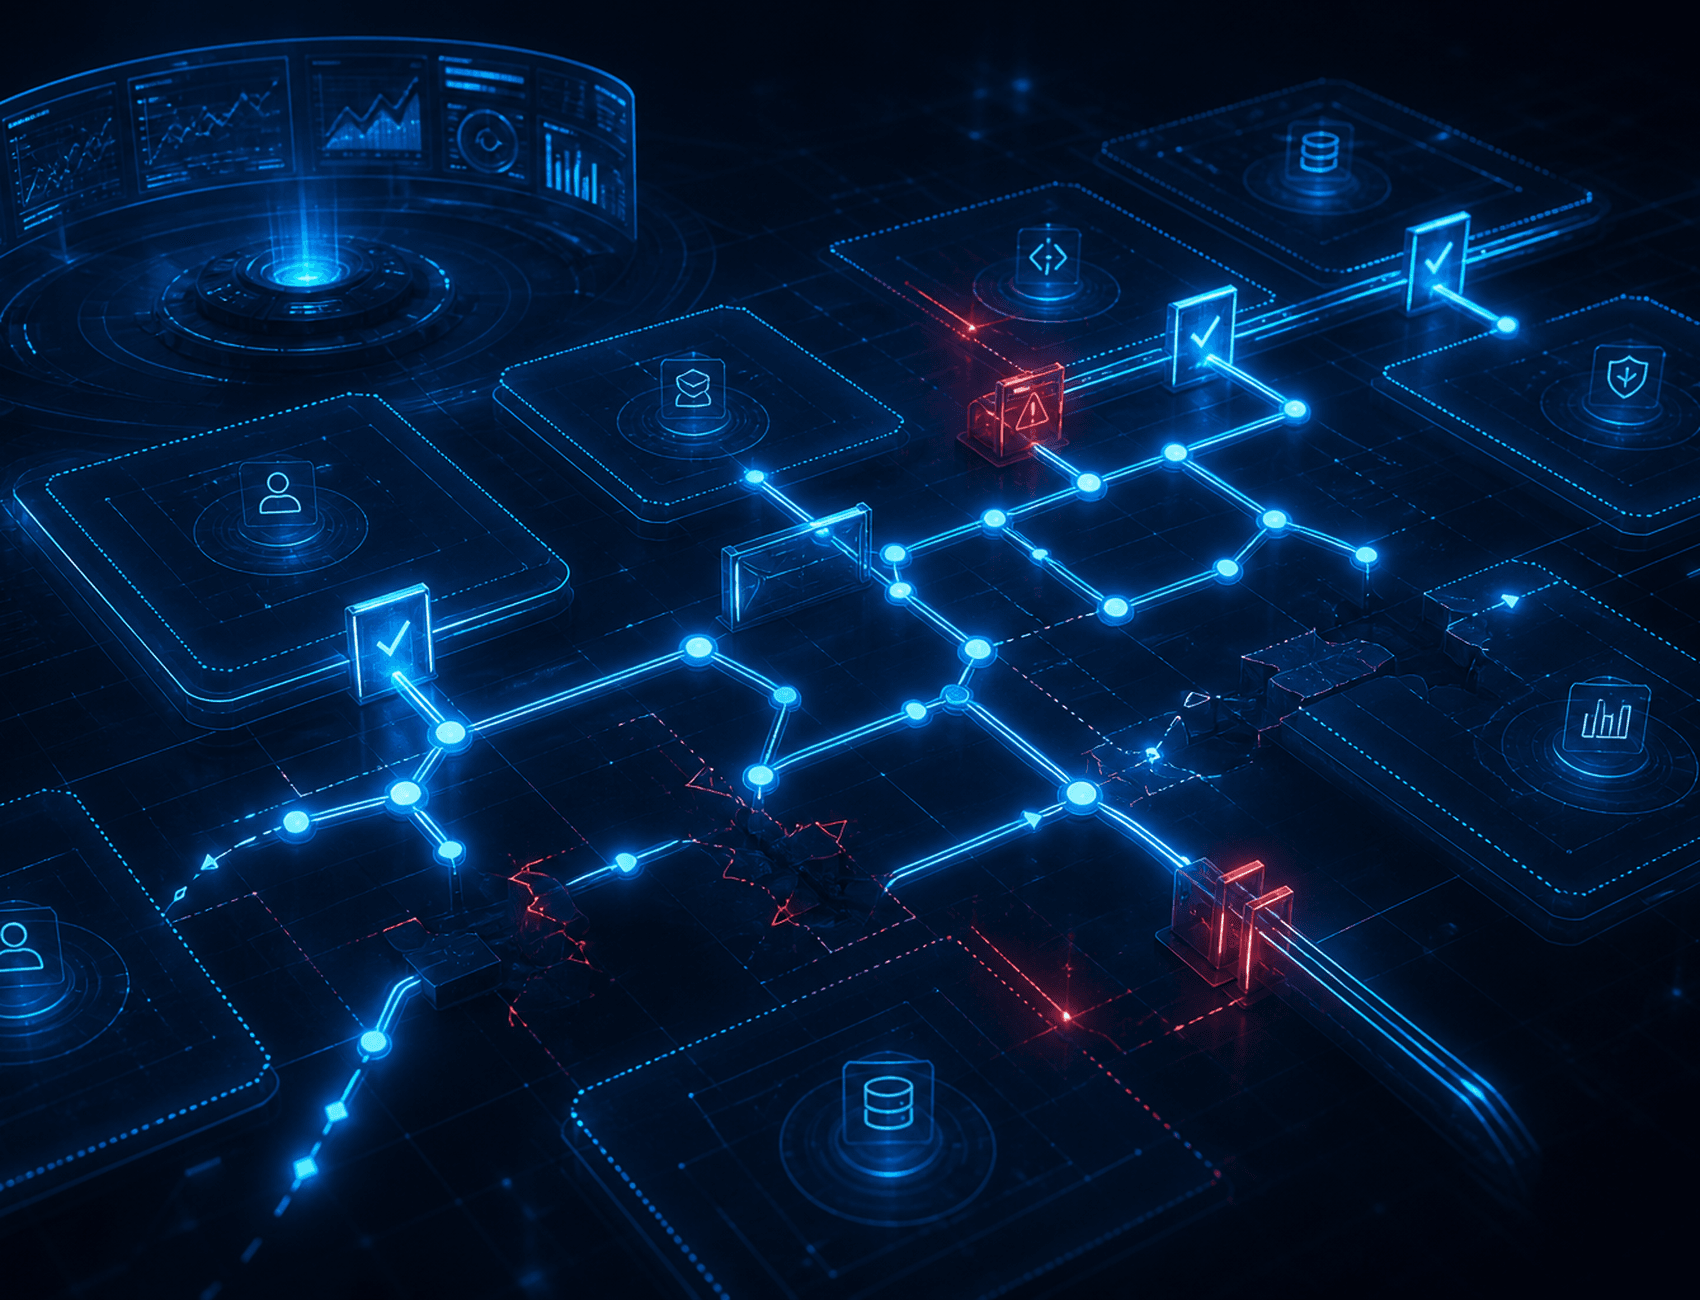
A checkpoint is a designed pause for validation. It is where the workflow asks
- Is the context sufficient?
- Is the result logically consistent?
- Is confidence high enough?
- Is human approval required?
- Has the system entered ambiguity or risk?
Without checkpoints, the workflow does not become efficient. It becomes blindly linear.
Checkpoints are what turn an AI system from a demo into an operational tool.
Important checkpoints every agent workflow should consider
Before tool use
The agent should confirm whether it actually has enough context to act.
After information retrieval
The system should check whether the sources are relevant, recent, and sufficient.
Before external action
Anything that affects customers, records, spending, publishing, or compliance should pass through an approval layer.
After completion
The system should log outcomes, exceptions, and failure reasons for future improvement.
A checkpoint is not friction for its own sake. It is a control layer that protects reliability.
Why fallback logic matters more than people think
An AI agent should never be designed as if everything will go well.
Real systems need fallback logic.
If the input is ambiguous, the agent should ask for clarification. If the data is missing, it should pause rather than invent. If tool access fails, it should log the issue and stop gracefully. If confidence is low, it should escalate. If a policy boundary is crossed, it should refuse or reroute.
This is what mature system design looks like.
A fragile agent assumes perfect conditions. A reliable agent assumes the environment will be messy and prepares for that reality.
That is often the difference between experimental AI and operational AI.
The hidden reason teams keep building chaotic agents
Many organizations are still thinking about agents through the lens of novelty instead of systems thinking.
They ask, “How much can this agent do?” They should first ask, “Under what conditions should this agent act?”
That shift matters.
Because the true value of AI agents is not maximum freedom. It is trustworthy delegation.
If a system cannot be trusted inside clear limits, giving it more autonomy only magnifies risk.
The strongest AI systems are usually not the most dramatic. They are the ones designed with disciplined scope, role separation, permission control, review logic, and failure handling.
Those systems may look slower in the demo stage. But they are the ones that survive real use.
How to build better AI agents in practice
If you want AI agents that are actually useful, design them like operating systems for decisions and actions, not like magical assistants.
Here are the core principles
- Define boundaries first
Be explicit about what the agent owns, what it cannot do, and when it must stop.
Design roles clearly
Separate research, analysis, drafting, reviewing, and execution where needed.
Restrict permissions
Give the agent only the access required for its narrow task.
Insert checkpoints
Add structured validation moments before risky or irreversible steps.
Add fallback logic
Plan for ambiguity, failure, missing context, and low confidence.
Log and improve
Track what the agent did, where it failed, and what conditions caused problems.
These are not just technical recommendations. They are management decisions. Good agent design is part engineering, part workflow design, and part governance.
AI agents do not fail because they are too advanced
They usually fail because the people designing them skip structure.
That is the uncomfortable truth behind many AI automation problems today. Teams want autonomous behavior without building operational clarity. They want outcomes without architecture.
But AI agents are not replacements for system thinking. They are stress tests for it.
If your boundaries are vague, your agents will drift. If your roles are blurred, your agents will overreach. If your permissions are broad, your agents will create risk. If your checkpoints are missing, your agents will fail silently until the damage becomes visible.
The future of useful AI agents will not belong to the teams that build the most chaotic autonomy.
It will belong to the teams that design the clearest structure.
Final thought
The best AI agent is not the one that appears the smartest.
It is the one that knows its role, respects its limits, and pauses before causing damage.
That is what makes an AI system reliable. And in real business environments, reliability matters far more than hype.