AI systems fail when they cannot explain their own work.
This does not mean every AI model must reveal every technical detail behind its output. Most users do not need a mathematical explanation of model behavior. But they do need something more practical: a clear account of how the system reached an output, what context it used, what assumptions shaped the result, what sources support it, and where human judgment must still take responsibility.
As AI moves from assistance to execution, explainability becomes an operating requirement. A chatbot that gives a weak answer is inconvenient. An AI workflow that updates a customer record, drafts a recommendation, changes a campaign, or summarizes a legal risk without traceability is a system problem.
The question is no longer only, "Can the AI produce the output?"
The better question is, "Can the organization understand and trust how that output was produced?"
The common mistake: treating explanation as a technical feature
Many teams think explainability belongs only to model researchers, compliance teams, or AI governance specialists.
That view is too narrow.
In real work, explanation is not only a technical concern. It is an operational concern. It affects whether a manager can review a recommendation, whether a team can correct a workflow, whether a customer-facing decision can be defended, and whether an organization can learn from mistakes.
If an AI system gives an answer without context, the user must either trust it blindly or redo the work manually. Both options reduce the value of automation.
Blind trust creates risk. Manual rework destroys leverage.
Mature AI systems need a middle layer: enough explanation for humans to inspect, challenge, improve, and own the result.
Output is not the same as work
A polished AI output can hide a weak process.
This is one of the biggest risks in applied AI. Fluent language creates confidence. A clean summary feels reliable. A structured recommendation looks professional. A dashboard description may sound strategic.
But fluency is not evidence.
The real work behind an AI output includes:
- which data was used
- which instructions guided the system
- which constraints were applied
- which assumptions were made
- which alternatives were ignored
- which risks were detected
- which human approved the final result
Without this layer, the organization cannot distinguish between useful automation and attractive guesswork.
This distinction matters because AI does not only generate content. It increasingly participates in knowledge work, customer operations, analysis, reporting, learning, and decision support. The more important the workflow becomes, the more explanation matters.
Explainability creates accountability
Accountability requires a trail.
If a human makes a decision, we can ask what they considered, why they chose a direction, what evidence they used, and what standard they applied. The same logic must exist around AI-supported work.
A team does not need to anthropomorphize the system. It does not need to pretend the AI has intentions. But it does need to know the operating path that produced the result.
For example:
- A sales summary should show which customer interactions it used.
- A marketing insight should connect back to campaign data or audience signals.
- A student feedback system should reveal what rubric shaped the comments.
- An internal agent should log which tool actions it took and why.
- A strategic recommendation should separate evidence from interpretation.
This is not bureaucracy. It is how trust becomes inspectable.
When explainability is missing, responsibility becomes vague. Users blame the AI. Leaders blame the team. Teams blame the tool. Nobody truly owns the outcome.
The explainability layer in AI workflows
Teams should design AI workflows with an explanation layer, not as an afterthought but as part of the system architecture.
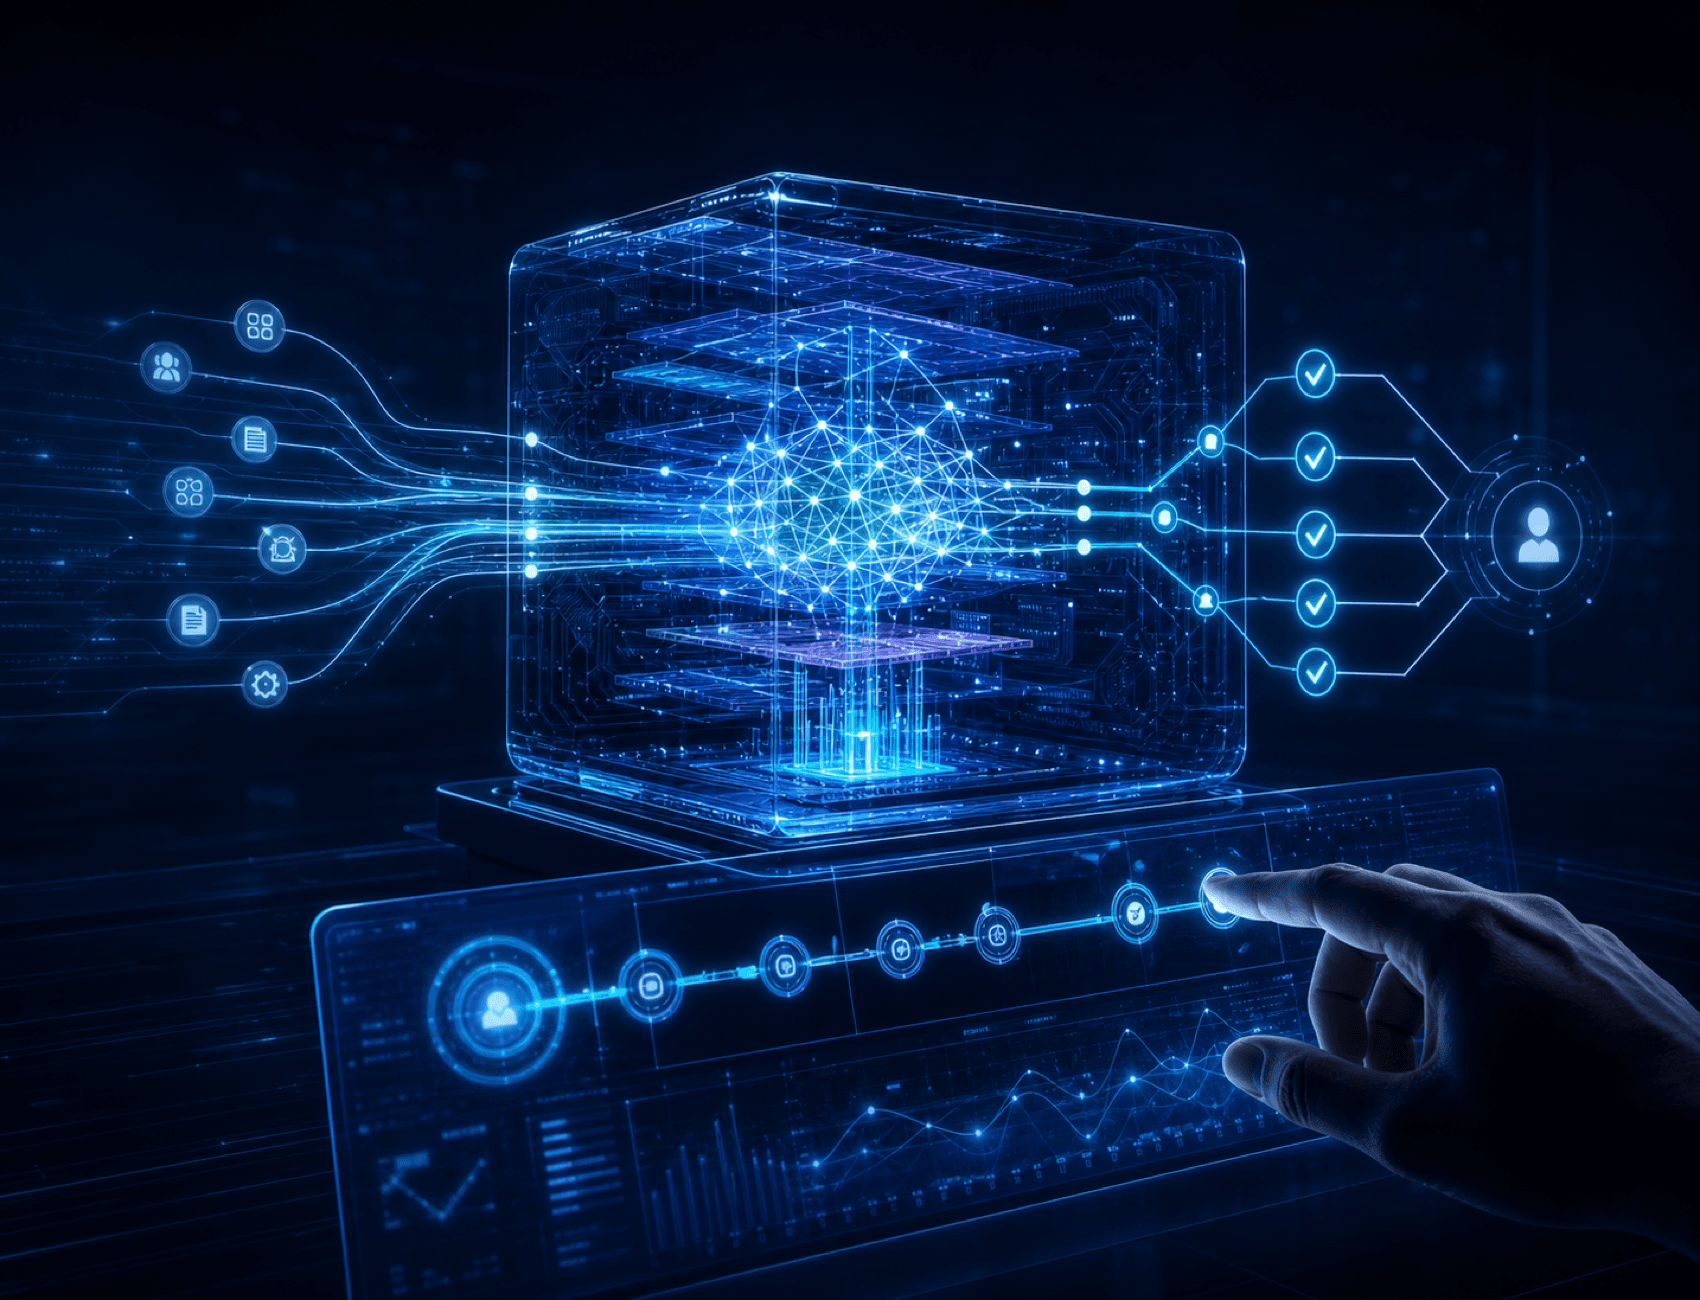
That layer should answer five practical questions.
1. What was the task?
The system should make the goal clear. A vague instruction creates vague work. If the task is ambiguous, the output should not appear more certain than the input deserves.
2. What context was used?
AI quality depends heavily on context. The system should show whether it used documents, customer data, past conversations, examples, policies, or external sources.
3. What reasoning path shaped the output?
This does not require exposing hidden model internals. It means summarizing the visible decision logic: what criteria mattered, what trade-offs were considered, and what assumptions affected the result.
4. What confidence or uncertainty remains?
A mature system should not present every answer with the same level of certainty. It should distinguish between verified facts, likely interpretations, weak signals, and areas needing human review.
5. Who owns the next step?
AI can assist execution, but responsibility must remain clear. The system should define whether the output is a draft, a recommendation, a completed action, or something requiring approval.
Why this matters more as agents become normal
Explainability becomes more important when AI systems move from answering to acting.
An agent may search, summarize, transform data, update a file, send a message, create a task, or trigger a workflow. Each step can be useful. Each step can also introduce error.
If an agent acts without a visible trail, the organization loses control over cause and effect. When something goes wrong, the team cannot easily answer:
- What did the agent do?
- What information did it rely on?
- Was the action authorized?
- Did it skip a required checkpoint?
- Did a human approve the final state?
This is why agentic AI should not be designed only around autonomy. It should be designed around accountable autonomy.
Autonomy without explanation creates anxiety. Explanation without ownership creates paperwork. The mature system needs both.
How teams should respond
Teams should start by separating low-risk outputs from high-stakes workflows.
Not every AI-generated paragraph requires a full audit trail. But workflows that affect customers, money, compliance, learning outcomes, employee decisions, or public claims need stronger explanation standards.
A practical framework looks like this:
- Define which AI outputs are drafts and which are decisions.
- Require source visibility for analysis, reporting, and recommendations.
- Add review checkpoints before external or high-impact actions.
- Log tool use and workflow steps for agentic systems.
- Teach teams to ask, "What is this output based on?"
The goal is not to slow AI down. The goal is to make speed trustworthy.
Conclusion
AI systems do not fail only because they make mistakes. They fail when people cannot understand, inspect, correct, or own the work they produce.
As AI becomes part of real workflows, explainability becomes less about technical curiosity and more about operational trust. Organizations need systems that can show their work in a way humans can review.
The future of applied AI will not belong only to the most capable models.
It will belong to the teams that can combine capability with context, traceability, human judgment, and clear accountability.
Key Takeaways
- AI explainability is an operational requirement, not only a technical feature.
- Fluent output can hide weak process, missing context, or unsupported assumptions.
- Agentic AI increases the need for visible trails, checkpoints, and ownership.
- Mature AI workflows should show task, context, reasoning path, uncertainty, and next-step responsibility.
FAQ
What does AI explainability mean in practical workflows?
It means users can understand what context, sources, assumptions, criteria, and actions shaped an AI output.
Does every AI output need full explainability?
No. Low-risk drafts may need lighter review, while high-impact workflows require stronger traceability and accountability.
Why is explainability important for AI agents?
Agents can take actions, not just produce answers. Teams need logs and checkpoints to understand what happened and who owns the result.