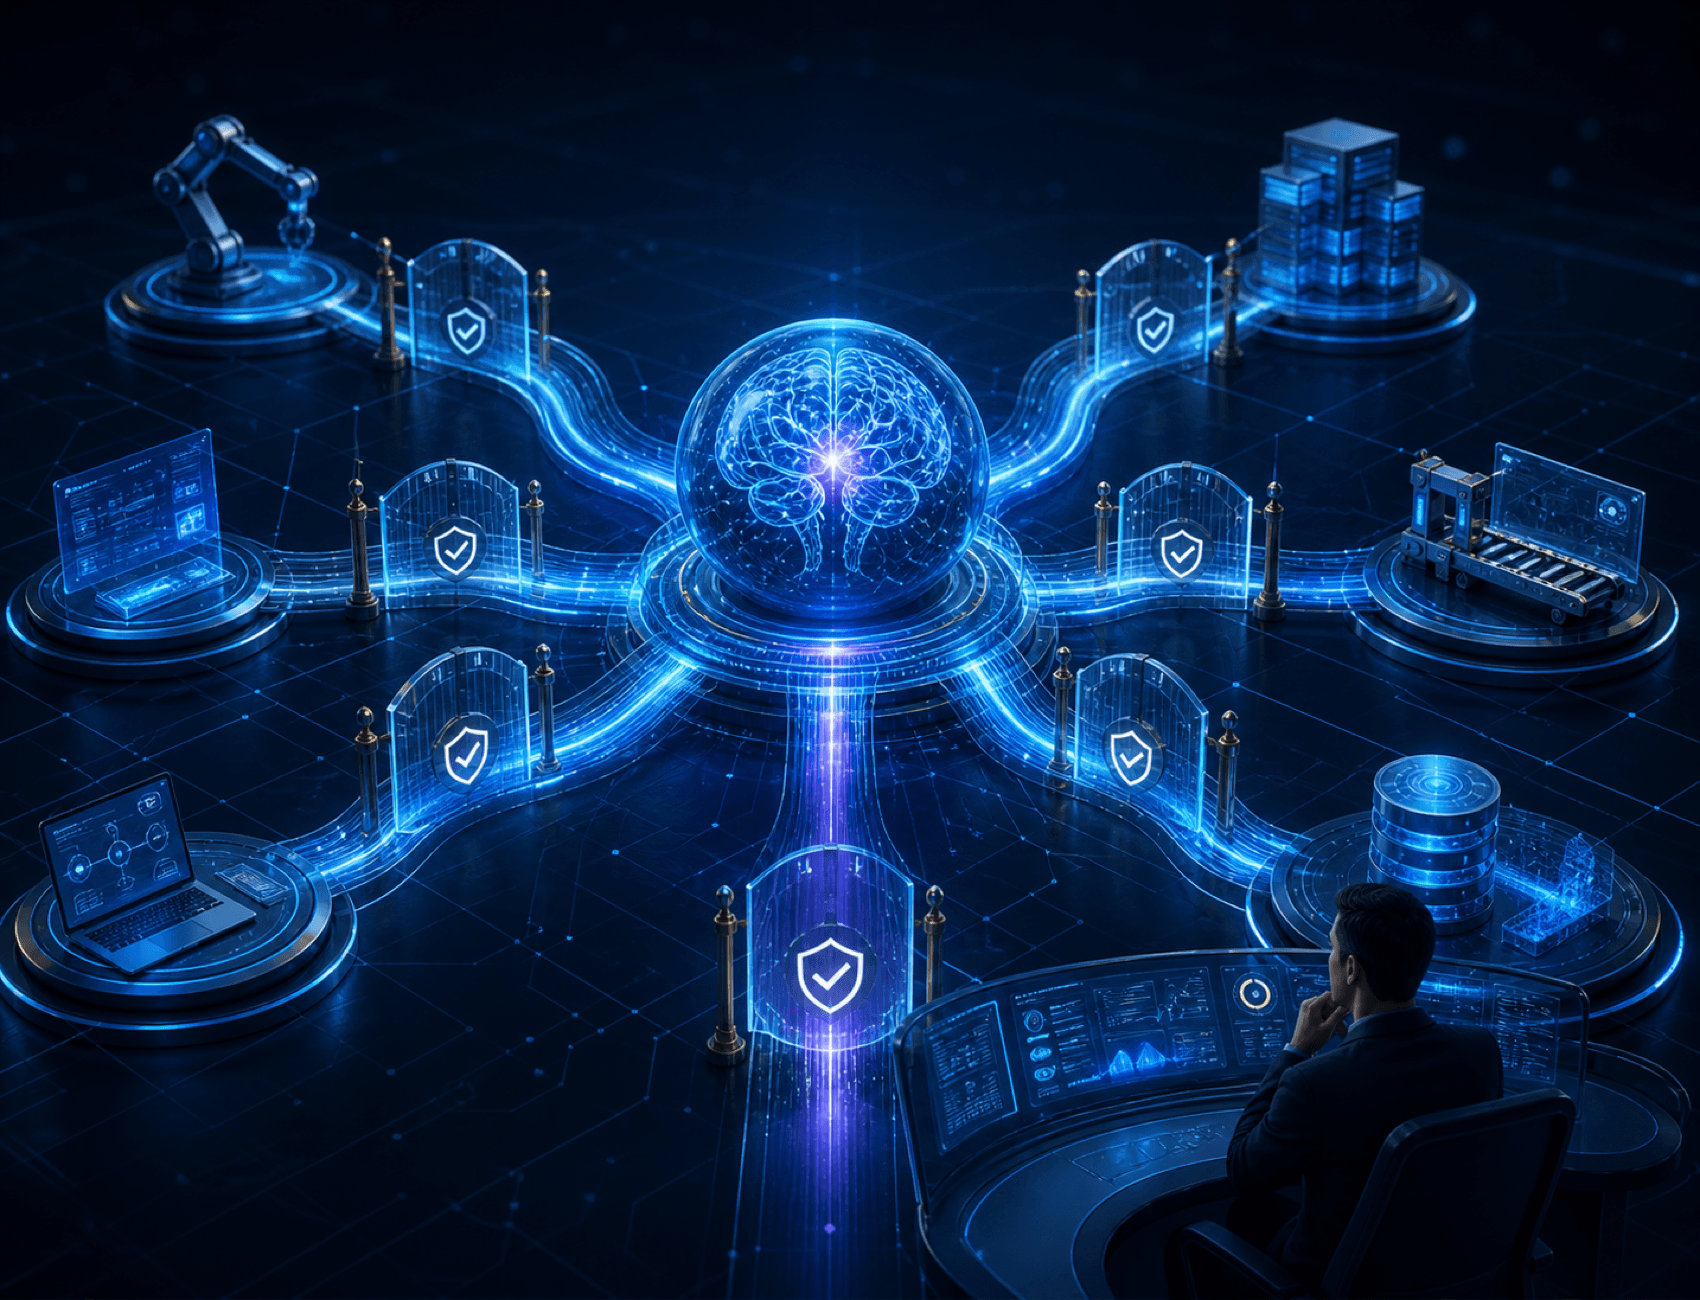
AI at work is crossing an important boundary. It is no longer used only to explain, summarize, or suggest. It is increasingly being asked to research, decide within defined limits, use tools, update systems, and complete work for human review.
OpenAI describes this shift as a move from assistance to execution. Its August 2026 enterprise research reports that leading firms are connecting agents to company context, tools, and repeatable workflows rather than treating AI as a standalone chat interface. That is a meaningful change. But it also exposes a deeper organizational problem.
The main bottleneck is no longer whether an AI model can perform a task. It is whether the organization knows how to delegate that task responsibly.
Most companies have spent years designing delegation for people. They have roles, approval levels, reporting lines, access permissions, and escalation paths. Very few have designed the equivalent for AI agents. As a result, they either give agents too little authority to create value or too much authority to remain trustworthy.
The next stage of enterprise AI will therefore depend less on prompt engineering and more on delegation architecture.
What delegation architecture means
Delegation architecture is the system that defines what an AI agent may do, what context it may use, what evidence it must produce, when it must ask for approval, and who remains accountable for the result.
It converts a vague instruction such as “use AI to improve operations” into an explicit operating model.
A mature delegation architecture answers six questions:
- What outcome is the agent responsible for producing?
- Which data, tools, and systems may it access?
- Which decisions may it make independently?
- Which actions require human approval?
- What conditions require escalation or shutdown?
- Who reviews performance and improves the workflow over time?
Without these answers, agent autonomy is mostly theatre. The agent may appear capable in a demonstration, but the organization cannot depend on it in production.
Why better models do not solve unclear delegation
A stronger model can reason better, use more tools, and sustain longer tasks. It cannot decide what the organization considers acceptable unless those boundaries have been made explicit.
Consider an AI sales agent. It may be technically capable of researching a prospect, scoring the lead, drafting an email, updating the CRM, and scheduling a follow-up. Yet capability does not answer the critical management questions.
May it contact the prospect without review? Which claims may it make? What happens when CRM data conflicts with public information? At what confidence level should it escalate? Who owns an inappropriate message or an incorrect qualification decision?
These are not model questions. They are operating-design questions.
When companies ignore them, they tend to fall into one of two failure modes.
The first is ceremonial autonomy. The agent is given an impressive label but requires approval at every step. Employees spend more time supervising the system than the system saves.
The second is unbounded automation. The agent is allowed to act without sufficient evidence, controls, or exception handling. Speed increases, but so does invisible risk.
Delegation architecture creates the productive space between these extremes.
The five layers of responsible AI delegation
1. Outcome boundaries
An agent needs a defined job, not a broad ambition.
“Improve customer experience” is not a delegable task. “Resolve billing inquiries that match approved policy and escalate disputed charges above a defined threshold” is.
The narrower definition creates measurable performance, clearer permissions, and a more reliable path to improvement.
2. Context boundaries
Agents perform better when they can access relevant organizational knowledge. But more context is not always better. Context should be both sufficient and authorized.
Teams need to specify which sources are trusted, how freshness is checked, how conflicting information is handled, and which sensitive data remains restricted. An agent connected to everything may be powerful, but it also becomes difficult to audit.
3. Decision boundaries
Not every decision deserves the same level of autonomy.
Low-risk, reversible decisions may be delegated. High-impact, ambiguous, or irreversible decisions should retain meaningful human review. The correct boundary depends not only on model accuracy but also on the cost of error, detectability of failure, and ease of recovery.
4. Evidence requirements
An agent should not merely produce an answer or action. It should leave enough evidence for a reviewer to understand what happened.
That may include sources used, assumptions made, tools called, rules applied, confidence signals, and reasons for escalation. Evidence turns AI output from an opaque event into a manageable decision process.
5. Learning ownership
Production use will reveal edge cases that no initial prompt or policy can anticipate. Someone must own the process of reviewing failures, updating rules, testing changes, and approving controlled rollout.
This is why deployment is not the end of an AI project. It is the beginning of an organizational learning loop.
A practical delegation test for leaders
Before giving an agent a workflow, leaders can apply a simple test.
Value: Is the outcome important enough to justify redesigning the workflow?
Clarity: Can the task, inputs, constraints, and success criteria be stated precisely?
Reversibility: If the agent is wrong, can the action be detected and reversed?
Evidence: Can the agent show how it reached the result?
Escalation: Are ambiguous or high-risk cases routed to the right person?
Ownership: Is a named human accountable for the system after launch?
A workflow that fails several of these tests is not ready for autonomous execution. It may still benefit from AI assistance, but autonomy should be earned through operating evidence rather than assumed from model capability.
The strategic implication
The organizations that gain the most from agents will not simply be those with access to the strongest models. Model access will continue to diffuse.
The durable advantage will come from knowing how to decompose work, encode judgment, connect trusted context, and create learning loops around delegated execution.
This is a management capability as much as a technical one. It requires leaders, operators, domain experts, risk owners, and technologists to design the system together.
Conclusion
Enterprise AI is moving from answering questions to completing work. That transition creates leverage, but it also changes the meaning of delegation.
The central question is no longer, “Can the agent do this?” It is, “Under what boundaries, with what evidence, and under whose accountability should the agent do this?”
Organizations that answer that question clearly can expand autonomy with confidence. Those that do not will oscillate between overcontrol and unsafe automation.
In the agentic era, delegation architecture is not a governance layer added after deployment. It is the operating system that makes execution possible.
Key Takeaways
- Enterprise AI is shifting from assistance to execution.
- The new constraint is the organization's ability to delegate responsibly, not model intelligence alone.
- Responsible delegation requires outcome, context, decision, evidence, escalation, and ownership boundaries.
- Agent autonomy should expand through operating evidence and reversibility.
- Delegation architecture will become a core management capability.
FAQ
What is AI delegation architecture?
AI delegation architecture is the operating system that defines an agent's job, permissions, decision limits, evidence requirements, approval points, escalation conditions, and human accountability.
How is it different from AI governance?
Governance defines broad principles and controls. Delegation architecture translates those principles into a specific workflow: who or what may act, under which conditions, and how performance is reviewed.
Should AI agents always require human approval?
No. Approval should depend on risk, ambiguity, reversibility, and the cost of error. Low-risk and reversible actions can earn greater autonomy; consequential decisions need stronger oversight.