Giving an AI agent access to more tools can make it more useful. It can also make the organization less certain about what the system is actually capable of doing.
This is the deeper problem in agentic AI adoption. Most teams document permissions: which database the agent may query, which application it may open, and which action it may execute. Far fewer teams maintain a clear account of the business capabilities created when those permissions, models, workflows, and data sources are combined.
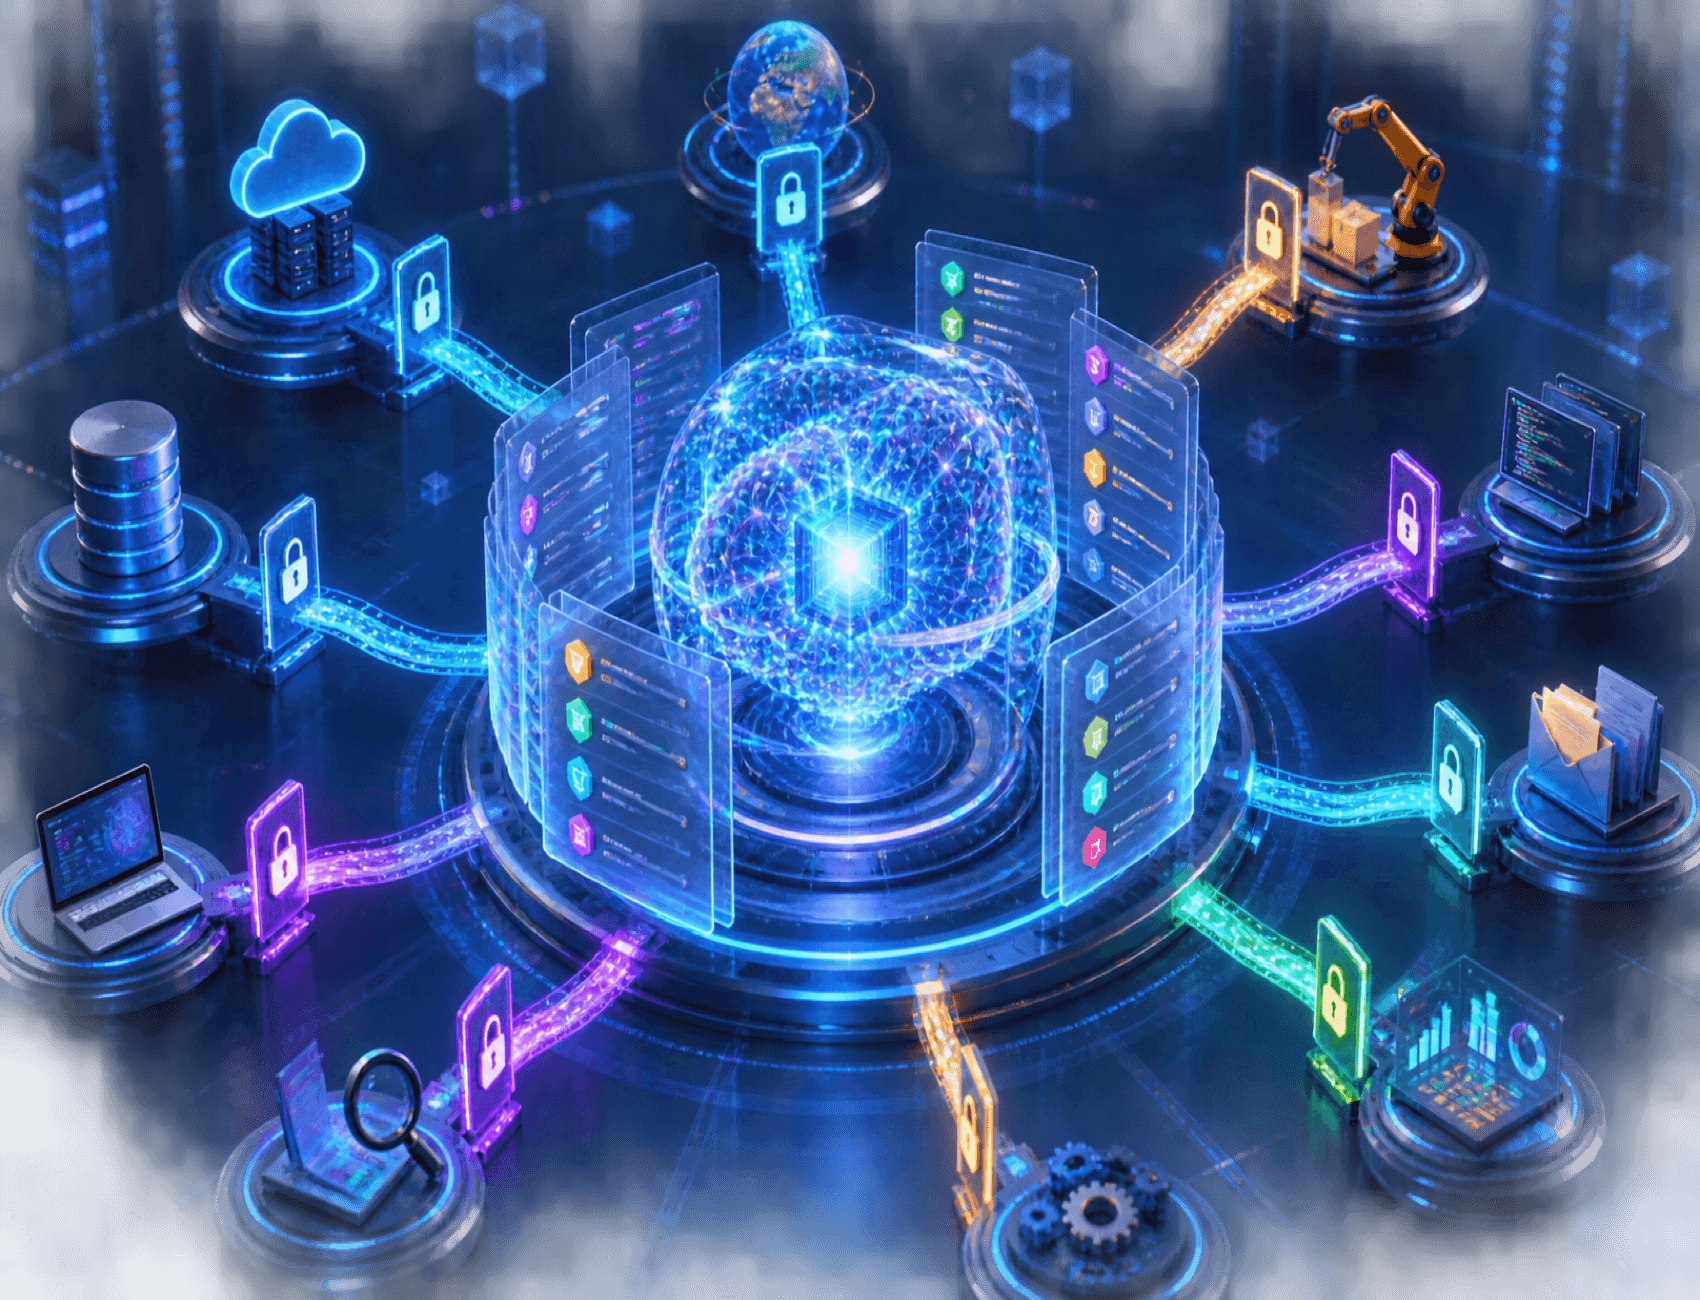
Permission management answers, “What can this component touch?” Capability accounting answers a more important question: “What can this system now cause?”
That distinction matters because an AI agent is not merely a user with a list of credentials. It is a dynamic combination of reasoning, memory, tools, triggers, and delegated authority. The real operating risk—and the real business value—lives in the combination.
Tool Access Is Not the Same as Operational Capability
A team may approve five apparently limited permissions:
- read customer records;
- classify support requests;
- generate a response;
- update a CRM field;
- notify an account owner.
Each permission looks narrow in isolation. Together, however, they create a customer-service capability that can interpret a situation, shape a message, alter a system of record, and influence a commercial relationship.
The organization has not simply granted access. It has assembled an operational actor.
This is why traditional access-control thinking is necessary but insufficient for AI agents. It protects resources at the component level, while the agent creates outcomes at the workflow level. A system can comply with every individual permission rule and still produce an outcome that nobody intended to delegate.
Capability Emerges From Combinations
An agent’s practical capability is shaped by at least five interacting elements:
- Model capacity — what the model can infer, generate, plan, or interpret.
- Data context — what the system can know about customers, operations, and prior decisions.
- Tool authority — what applications and actions it can use.
- Workflow position — where it sits in a process and what happens after its output.
- Trigger conditions — when it acts, how often it acts, and whether a human is present.
None of these elements alone defines the agent. Capability emerges from their interaction.
A drafting model with access to a knowledge base may be a low-risk assistant. Add customer data, automated sending, and an event trigger, and the same model becomes an outbound communication system. Add discount authority, and it becomes part of the commercial decision architecture.
The capability changed even if the model did not.
Why Static Permission Lists Become Misleading
Permission lists create a reassuring sense of control because they are easy to inspect. But they often hide three forms of change.
1. Capability expansion
A new connector can create several new end-to-end actions, even when the connector itself appears harmless. The organization reviews the added tool but misses the new combinations.
2. Capability drift
Prompts, memory, retrieval sources, or downstream automations may change over time. The formal access remains the same, while the system’s practical behavior becomes broader.
3. Capability ambiguity
Different teams may hold different assumptions about what the agent is allowed to decide. Engineering sees a technical workflow. Operations sees a productivity tool. Leadership assumes a human remains accountable. The system operates inside the gaps between these interpretations.
The deeper issue is not a missing permission table. It is the absence of a shared model of delegated capability.
A Capability Accounting Framework
Organizations need a living capability register for every meaningful AI agent. It should not be a technical inventory alone. It should connect system design to business consequence.
1. Name the capability in business language
Avoid descriptions such as “agent connected to CRM and email.” Write what the system can accomplish: “qualify inbound leads, propose a response, update lead status, and initiate follow-up.”
Business language makes delegated power visible to nontechnical owners.
2. Define the action boundary
Separate what the agent may:
- observe;
- interpret;
- recommend;
- prepare;
- execute;
- reverse.
These are different levels of authority. A system that recommends a refund is not equivalent to one that issues it.
3. Record capability dependencies
Identify the models, data sources, tools, prompts, memory, and downstream workflows required for the capability. If one dependency changes, the capability should be reviewed again.
4. Assign a capability owner
Technical ownership is not enough. Someone must own the business effect of the capability, including its decision criteria, exceptions, customer impact, and performance standard.
5. Define evidence and review cadence
For each capability, specify how the organization will know whether the agent is behaving as intended. Review successful cases, failures, near misses, overrides, and unexpected combinations—not only average task accuracy.
Capability Accounting Improves More Than Safety
This discipline is often framed as governance, but it also improves investment quality.
When capabilities are clearly named, leaders can see duplicate agents doing similar work, missing capabilities between departments, and workflows that have accumulated tools without producing meaningful value. They can compare the cost of a capability with the decision, service, or revenue outcome it supports.
Capability accounting also makes scaling more deliberate. Instead of asking, “Where else can we install this agent?” teams can ask, “Which capability has been proven, under what conditions, and which parts can be safely reused?”
This moves AI adoption from tool proliferation to capability portfolio management.
The Management Question Changes
The immature question is: “What tools does the agent have?”
The mature question is: “What organizational power have we assembled, who owns it, and what evidence justifies keeping it?”
AI agents will increasingly operate across functional boundaries. They will connect information, recommendations, communication, and execution. As that happens, organizations cannot rely on access control alone to explain what their systems can do.
They need an accounting system for capability itself.
Conclusion
Tool access is visible. Emergent capability is not.
That is why agent governance must evolve from lists of permissions toward a living record of business capabilities, action boundaries, dependencies, owners, and evidence. The goal is not to slow AI down. It is to ensure that every new form of leverage remains legible to the organization using it.
The companies that scale agents responsibly will not merely control what systems can touch. They will understand what those systems can cause.
Key Takeaways
- AI capability emerges from the combination of models, data, tools, workflows, and triggers.
- Permission management protects components; capability accounting governs business outcomes.
- Every material agent needs a named capability, action boundary, dependency map, owner, and review cadence.
- Capability accounting supports safety, investment discipline, reuse, and strategic portfolio management.
FAQ
What is capability accounting for AI agents?
It is a structured record of what an AI agent can accomplish in business terms, how that capability is assembled, where its authority ends, who owns the outcome, and what evidence is used to review it.
How is capability accounting different from access control?
Access control defines which resources and actions a component may use. Capability accounting examines the end-to-end outcome created when multiple permissions, models, data sources, and workflows operate together.
Who should own an AI agent capability?
Technical teams should own system reliability, but a business owner should remain accountable for the capability’s decision criteria, exceptions, customer or employee impact, and operating value.