AI agents do not become enterprise-ready simply because they can use more tools. They become enterprise-ready when the organization can determine what each agent is allowed to do, under which conditions, with whose approval, and with what path to reversal.
This is the practical meaning of authorization architecture for AI agents: a system of identities, permissions, approval thresholds, escalation rules, audit records, and revocation controls that governs agent action.
The distinction matters because an agent is not only a model producing an answer. It can retrieve confidential information, update a customer record, approve a transaction, send a message, or trigger another workflow. Once AI moves from generating content to changing business state, access is no longer a convenience feature. It is a management decision encoded in infrastructure.
The Common Misconception: More Connections Create More Value
Many organizations evaluate agents by counting integrations. An agent connected to email, CRM, documents, analytics, finance, and project management appears more capable than one with limited access.
But connection breadth is not the same as operational maturity.
Every new tool expands both the agent's usefulness and its action surface. A tool may expose multiple resources. A resource may allow several operations. Each operation may carry different business consequences depending on the data, customer, timing, and user involved.
“The agent can access Salesforce” is therefore not a sufficient policy. The real questions are more specific:
- Which Salesforce objects can it read?
- Which fields can it modify?
- Can it act for every account or only assigned accounts?
- Can it send an external message without review?
- What happens when confidence is low or instructions conflict?
- Who can suspend the agent immediately?
Without answers, the organization has connectivity but not control.
What Authorization Architecture Actually Includes
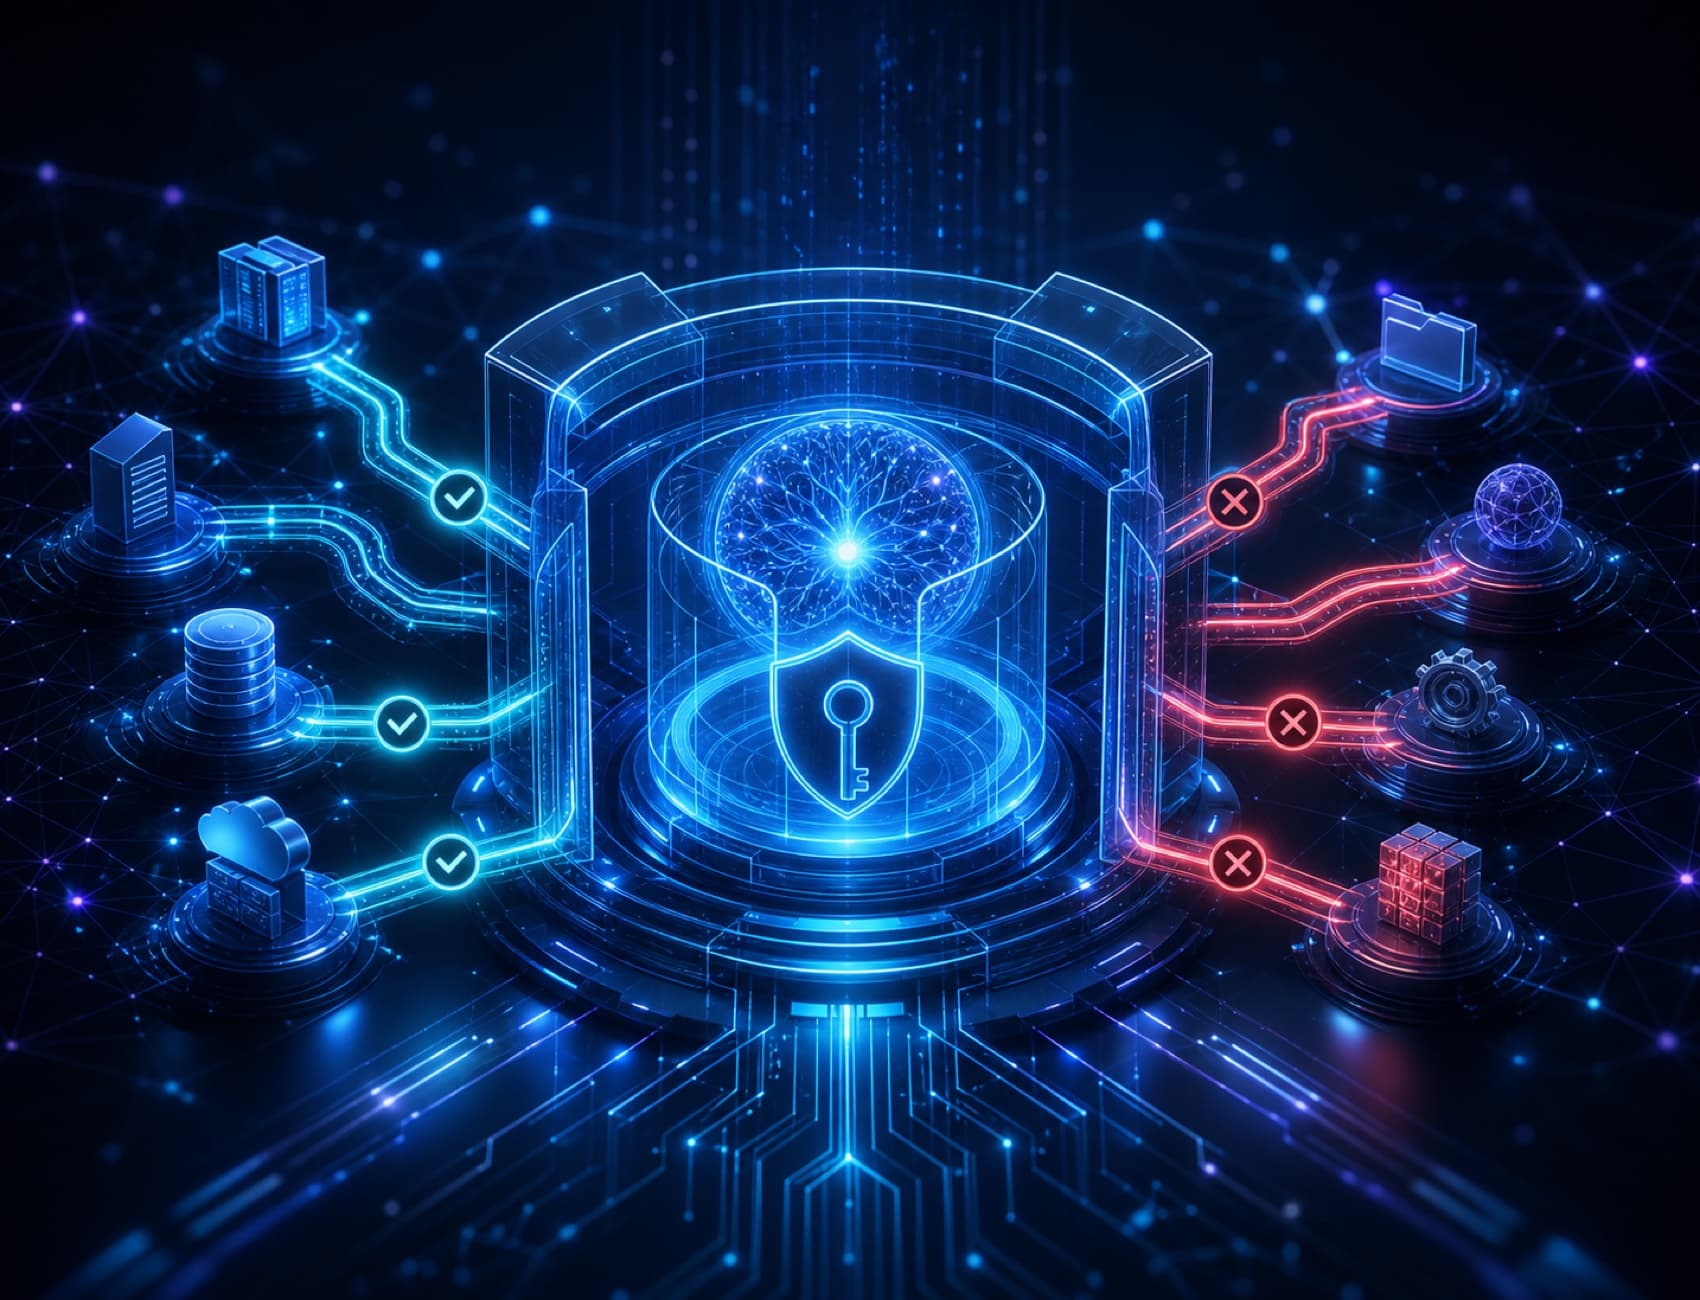
Authorization architecture is the decision system between an agent's capability and its action.
It should include at least five layers.
1. A distinct identity
Every production agent should act through an identifiable service identity rather than borrowing a human user's broad credentials. A distinct identity makes permissions inspectable and activity attributable.
2. Minimum necessary scope
Permissions should be limited by tool, resource, operation, data class, time, and business context. A sales research agent may need to read public account information, but it does not automatically need permission to change opportunity stages or export an entire customer database.
3. Risk-based approval thresholds
Not every action requires the same friction. Reading a public document, drafting an internal summary, sending an external contract, and approving a payment have different consequence levels.
Approval policy should become stricter as reversibility decreases, external impact increases, or sensitive data becomes involved.
4. Escalation and refusal rules
An agent needs explicit conditions for stopping. Ambiguous identity, missing evidence, conflicting instructions, unusual transaction value, or an unavailable reviewer should trigger escalation rather than improvisation.
5. Audit and revocation
The organization must be able to reconstruct what the agent saw, which policy applied, what it attempted, what was approved, and what changed. It must also be able to revoke access without dismantling the entire workflow.
Why Static Role-Based Access Is Not Enough
Traditional role-based access control remains useful, but agents introduce more dynamic context.
A human employee may hold a stable role. An agent can be invoked by different users, work across multiple systems, receive untrusted external content, and chain actions faster than a reviewer can observe them.
This means permission should often depend on both identity and context:
- who requested the action;
- which customer or dataset is involved;
- whether the action is internal or external;
- the monetary or reputational consequence;
- whether the output is reversible;
- whether the evidence meets a defined threshold.
The mature question is not only, “Can this agent perform this action?” It is, “Should this agent perform this action in this specific situation?”
A Practical Authorization Design Framework
Leaders can use the I-SAFE framework before allowing an agent to operate in production.
Identity
Give the agent a distinct identity. Define who owns it and who is accountable for its behavior.
Scope
List the exact systems, resources, operations, and data classes it may access. Remove permissions that are merely convenient.
Approval
Classify actions by consequence. Define which actions are automatic, which require review, and which are prohibited.
Failure response
Specify escalation, timeout, refusal, rollback, and incident procedures. A safe agent must know when not to continue.
Evidence
Retain enough context to explain and audit the action: request, retrieved information, policy decision, approval, tool call, and outcome.
This framework converts governance from a general principle into an operational contract.
Strategic Implication: Agent Governance Must Exist Before Scale
Recent enterprise AI announcements increasingly emphasize agent control planes, audit trails, session governance, and governed access. This is a signal that the market is moving beyond agent demonstrations toward production accountability.
Organizations should not treat authorization as a security layer added after an agent proves useful. Authorization shapes which uses are safe enough to scale in the first place.
The teams that move fastest over time will not be those that remove every constraint. They will be those that make constraints precise enough for trustworthy autonomy.
Conclusion
An AI agent's real power is not the number of tools it can reach. It is the number of valuable actions it can complete within clear boundaries.
More access increases possibility. Authorization architecture converts possibility into responsible operating capacity.
The future of enterprise agents will therefore depend less on unrestricted autonomy and more on explicit identity, contextual permission, human approval, reliable escalation, and reversible action. Trust at scale is not created by asking an agent to behave well. It is created by designing the conditions under which it is allowed to act.
Key Takeaways
- Authorization architecture governs who an agent is, what it may do, when approval is required, and how access is revoked.
- Tool connectivity without granular permission design expands operational risk.
- High-consequence, external, sensitive, or irreversible actions require stronger controls.
- Distinct identities, minimum scope, escalation rules, audit evidence, and revocation are core production requirements.
- Mature autonomy is bounded autonomy.
FAQ
What is authorization architecture for AI agents?
It is the system of agent identities, permissions, contextual policies, approvals, escalation rules, audit records, and revocation controls that determines whether an agent may perform a specific action.
How is authorization different from authentication?
Authentication confirms the identity of an agent or user. Authorization determines what that authenticated identity is permitted to access or change.
Should every AI agent action require human approval?
No. Low-risk and reversible actions can often run automatically. Approval should increase with sensitivity, external impact, financial consequence, uncertainty, and irreversibility.
What is the principle of least privilege for AI agents?
It means giving an agent only the minimum access necessary to complete its defined task, for the minimum required context and duration.