Many organizations are excited about AI agents because agents appear to promise autonomy.
They can search, analyze, draft, compare, call tools, update systems, and complete sequences of work with less human prompting. This creates the impression that the next advantage will belong to the organization that gives agents more freedom.
That is only partly true.
AI agents do not become strategically valuable because they are autonomous. They become valuable when autonomy is governed by clear operating rules.
This distinction matters because agentic systems do not only produce outputs. They act inside workflows. They touch data, customers, internal tools, brand communication, business decisions, and sometimes public-facing systems. When agents move from suggestion to action, the core question changes.
The question is no longer only: can the agent do the task?
The better question is: under what rules should the agent be allowed to act?
Autonomy Without Rules Creates Fragile Leverage
The easiest mistake is to treat autonomy as the goal.
A team may build an agent that can create reports, send emails, update CRM records, generate campaign ideas, or summarize customer feedback. Technically, this looks impressive. Operationally, it may save time. But strategically, it can also create a new layer of risk.
An agent can move quickly in the wrong direction. It can act on incomplete context. It can apply an outdated rule. It can overgeneralize from weak data. It can make a recommendation that sounds confident but violates the brand, the workflow, or the real business priority.
This is why agent governance matters.
Governance is not a layer of bureaucracy added after innovation. It is the operating system that makes autonomy usable.
Without governance, agents become powerful but unstable assistants. With governance, they become reliable participants in a decision workflow.
The Real Problem Is Not Capability
Most AI adoption discussions focus on capability.
Can the agent use the browser? Can it read files? Can it write code? Can it connect to a CRM? Can it generate images? Can it call APIs? Can it operate across tools?
These are useful questions, but they are not sufficient.
Capability tells us what an agent can do. Governance tells us what it should do, when it should stop, who is accountable, and how the system learns from its behavior.
Many teams are already close to having enough capability. The harder challenge is deciding how that capability should be constrained, supervised, evaluated, and improved.
The bottleneck is not always model intelligence.
The bottleneck is operating discipline.
Operating Rules Define Trust
An operating rule is a clear standard that shapes how an agent behaves inside a workflow.
It may define what data the agent can access, what action it can take without approval, what decisions require human review, what tone it must preserve, what sources it can trust, what claims require verification, and what situations must be escalated.
For example, an AI marketing agent may be allowed to draft three campaign angles, analyze audience comments, and suggest positioning improvements. But it should not publish public content, change ad budgets, or make brand claims without review.
An AI sales agent may be allowed to qualify leads, prepare outreach drafts, and summarize account history. But it should not promise discounts, modify contracts, or send sensitive proposals without approval.
These rules do not weaken the agent.
They make the agent usable in the real world.
Good Governance Separates Risk Levels
Not every task needs the same level of control.
Some agent actions are low-risk. Formatting a report, summarizing a meeting, generating draft options, cleaning a spreadsheet, or preparing a checklist may require only light supervision.
Some actions are medium-risk. Recommending a campaign direction, drafting client communication, interpreting analytics, or updating internal records may require review.
Some actions are high-risk. Publishing externally, contacting customers, making financial decisions, changing strategic priorities, or handling private data should require explicit human control.
A mature AI workflow separates these levels.
The goal is not to slow everything down. The goal is to match autonomy with consequence.
When the consequence is low, automation can move faster. When the consequence is high, judgment must become stronger.
Governance Should Be Built Into the Workflow
Many organizations treat governance as a policy document.
That is not enough.
If the rules only live in a document that people rarely read, they will not shape behavior. Agent governance must be embedded into the workflow itself: prompts, system instructions, tool permissions, review checkpoints, logging, evaluation rubrics, and escalation paths.
The workflow should make the right behavior easier than the wrong behavior.
For example, an agent should know when to ask for approval. It should preserve a record of its sources. It should explain the reasoning behind important recommendations. It should mark uncertainty instead of hiding it. It should refuse to act when context is missing. It should route high-risk decisions back to a human.
This is how governance becomes operational.
It moves from principle to practice.
Human Judgment Moves From Inspection to Design
Many teams imagine human oversight as final inspection.
The agent works. The human checks.
This model is useful for small tasks, but it does not scale well. If every agent output requires manual inspection, the organization loses much of the promised leverage.
The better model is judgment by design.
Humans should define the criteria before the agent acts. They should design the rules, examples, boundaries, review points, and success measures that guide the workflow. They should spend less time correcting every output and more time improving the system that produces outputs.
This does not remove accountability.
It makes accountability clearer.
The human remains responsible for the rules, the approval structure, and the final consequences of meaningful decisions.
A Practical Agent Governance Framework
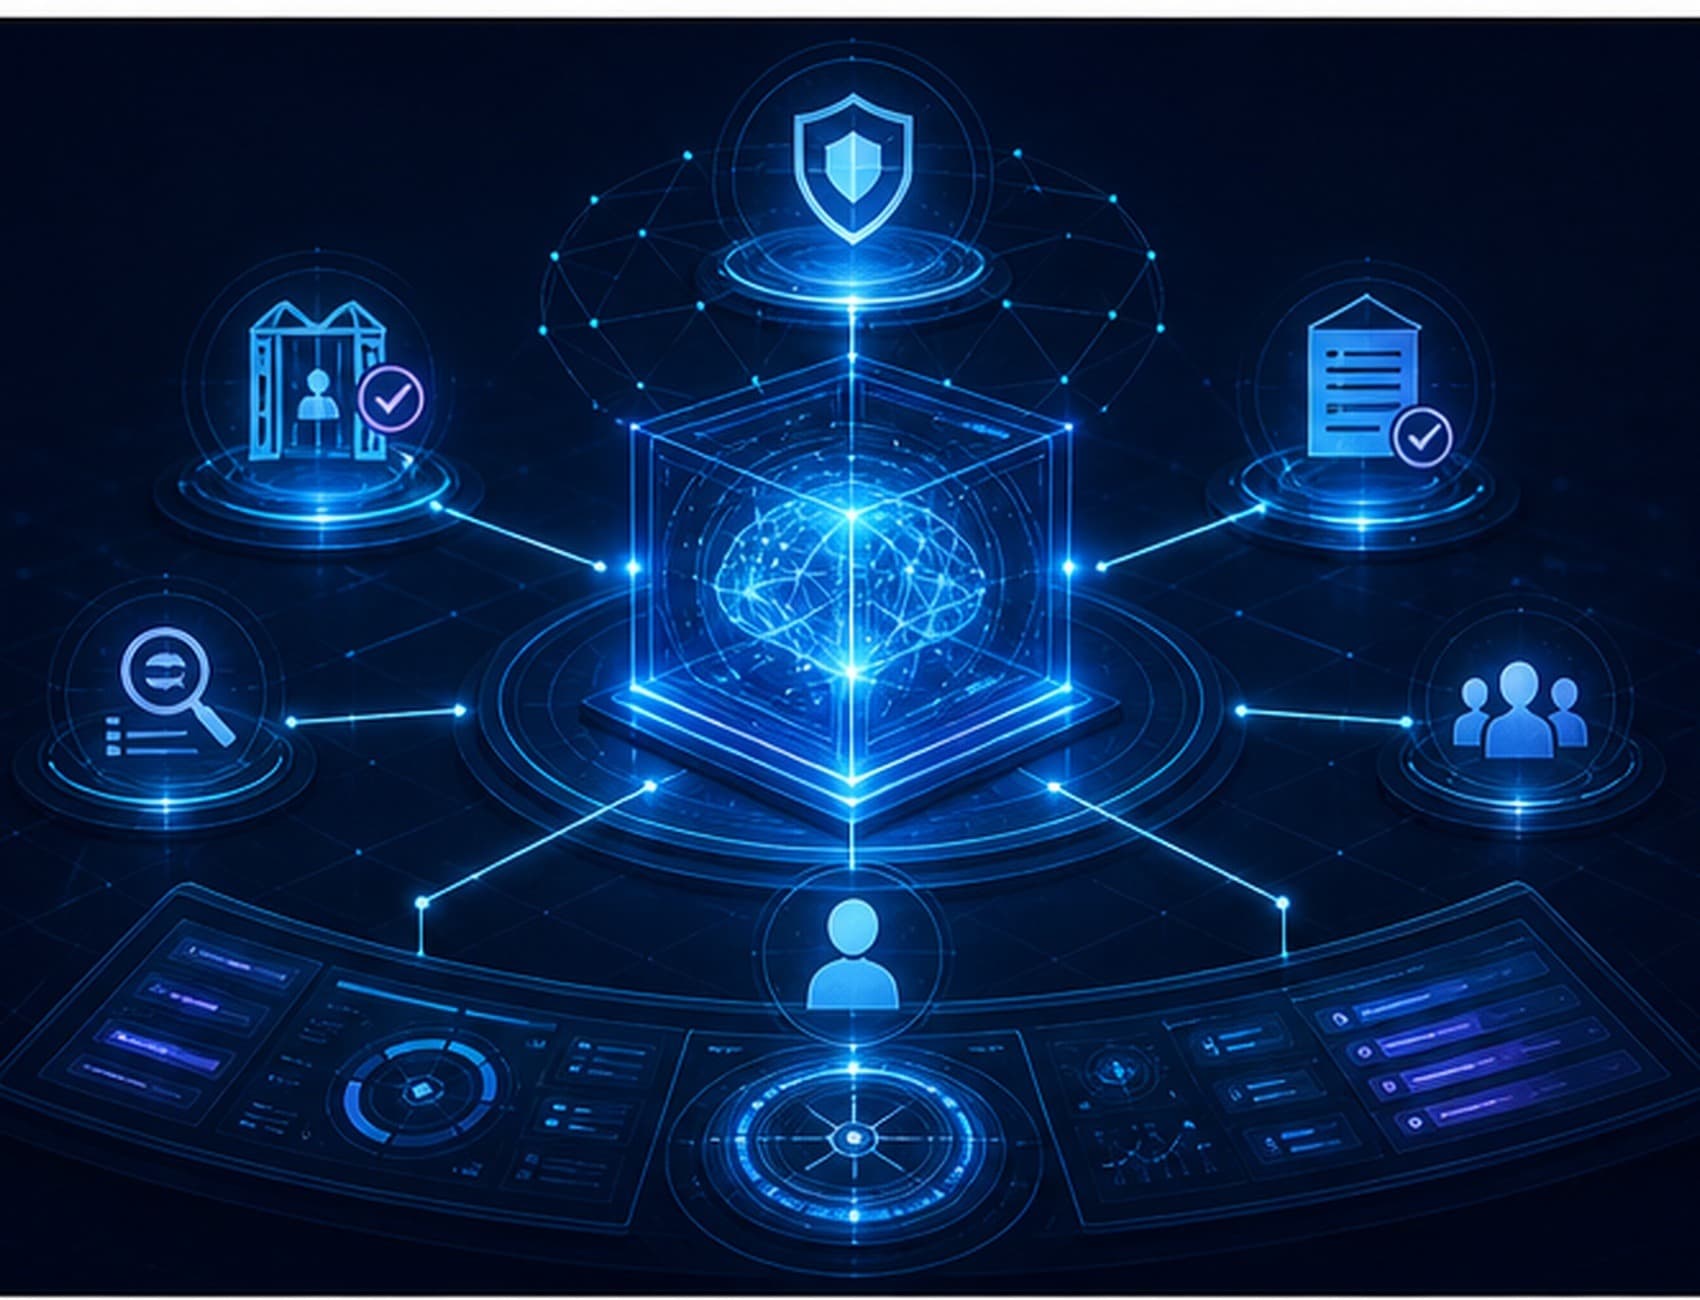
Organizations can start with five questions.
1. What decisions can the agent influence?
An agent that only drafts text is different from an agent that recommends strategy or updates business systems. Define the decision surface before defining the tool access.
2. What context must the agent use?
The agent should not guess from generic knowledge when internal standards matter. Provide brand guidelines, workflow rules, customer context, examples, and decision criteria.
3. What actions require approval?
Separate suggestions, drafts, internal updates, external communication, and irreversible actions. Each level needs a different rule.
4. What must be logged?
If an agent affects a workflow, the organization should know what it did, why it did it, what sources it used, and where a human approved or changed the result.
5. How will the system improve?
Governance should include feedback. Mistakes should become new rules. Good decisions should become examples. Repeated review comments should become workflow improvements.
Final Thought
AI agents will not create serious advantage simply because they can act independently.
Autonomy is only useful when it is surrounded by context, permissions, review, and accountability.
The organizations that win with agents will not be the ones that remove humans from every workflow. They will be the ones that design better operating rules so human judgment and machine capability can work together with clarity.
Agent governance is not a brake on innovation.
It is the structure that lets innovation become trustworthy.