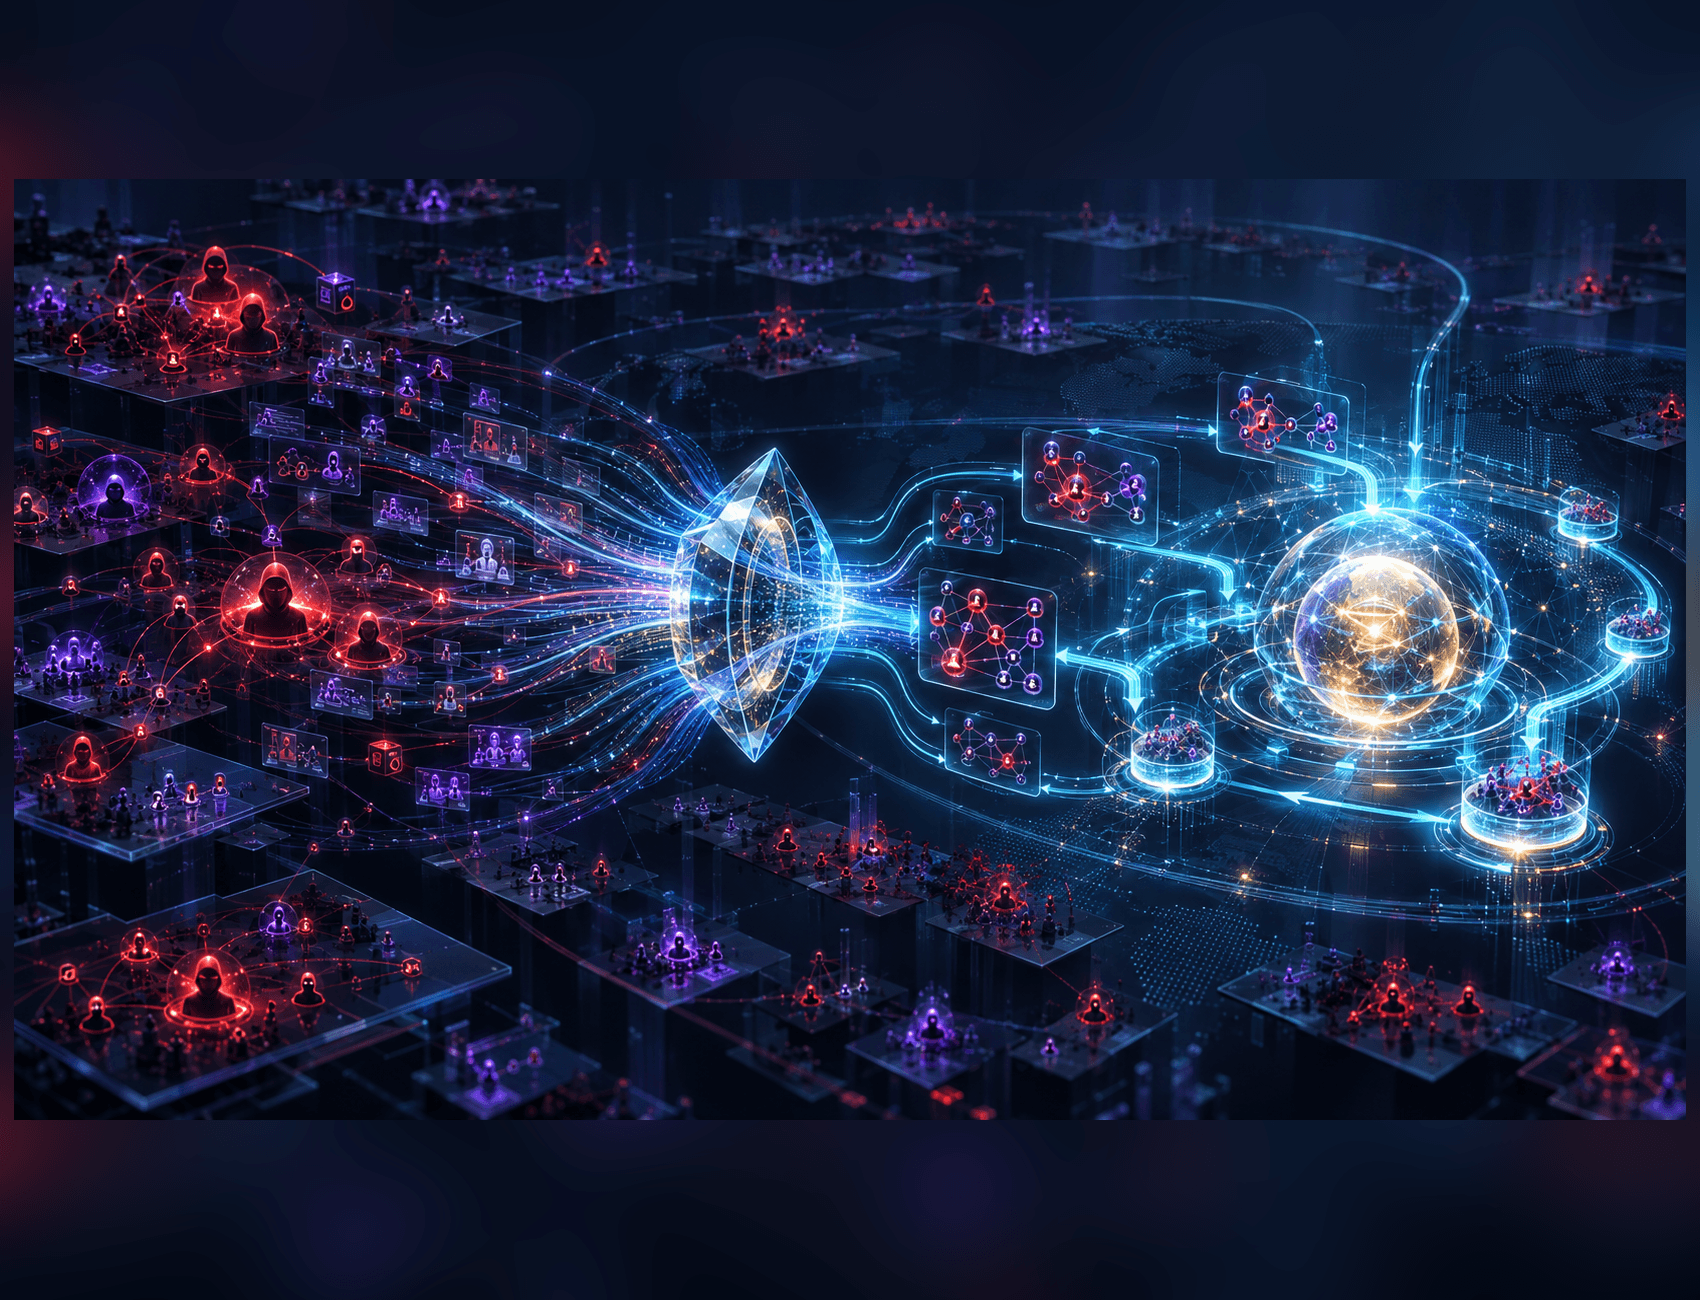
Trademark registration establishes a legal right. It does not create continuous visibility into how that right is being attacked across marketplaces, social platforms, livestreams, messaging applications, search results, and advertising networks.
That gap is becoming strategically important.
Counterfeit sellers and impersonators do not operate like traditional competitors. They change accounts, images, domains, payment routes, product descriptions, and fulfilment locations. They exploit the speed and fragmentation of digital commerce.
The deeper issue is threat intelligence.
**Digital brand threat intelligence is the continuous process of detecting, connecting, prioritising, and acting on signals of impersonation, counterfeiting, deception, and intellectual-property misuse across digital channels.**
Recent enforcement data from Can Tho illustrates the scale and migration of the problem: more than 210 intellectual-property infringement cases were detected, while authorities highlighted growing violations across e-commerce platforms, livestreams, social media, and mobile applications. Registration remains essential, but protection now depends on how quickly weak signals become coordinated action.
Legal ownership is the starting point
A registered trademark, design, geographical indication, or certification mark gives the owner a legal basis for enforcement. Without that basis, takedowns and claims become harder.
But a certificate does not answer operational questions:
- Where is the brand being impersonated today?
- Which seller accounts belong to the same network?
- Which counterfeit offer is causing the greatest customer harm?
- What evidence will a platform, regulator, or court accept?
- Which channel should be contacted first?
- Has the infringement disappeared or moved elsewhere?
- What customer confusion remains after the listing is removed?
These are intelligence and response questions.
The distinction resembles [brand claim maintenance](/blog/brand-claim-maintenance). A brand claim does not remain trustworthy because it was once approved. It must be monitored against changing reality. Intellectual-property protection has the same operating requirement.
Digital infringement behaves like a network
Traditional enforcement often begins with an individual violation: a shop, product, package, advertisement, or domain.
Online infringement is rarely isolated.
One operator may control multiple storefronts. Several sellers may use the same images, contact details, payment account, warehouse, or fulfilment partner. When one account is removed, inventory and traffic can move to another within hours.
The visible listing is therefore an event, not the full threat.
Brands need to connect signals across:
- seller identities and account creation patterns;
- reused product photography and video;
- pricing anomalies and unusual promotion cycles;
- domains, phone numbers, payment details, and delivery points;
- customer complaints and warranty claims;
- paid advertisements and influencer content;
- search terms used to imitate or divert demand;
- geographic and logistics patterns.
Connecting these signals transforms enforcement from repeated takedowns into network disruption.
Build a brand threat intelligence loop
A practical system contains six stages.
1. Define protected brand assets
The organisation should maintain an operational registry of trademarks, packaging, designs, product images, certification marks, official accounts, authorised sellers, domains, and approved claims.
This is not only a legal archive. It is the reference layer used by monitoring teams, platforms, agencies, distributors, and customer service.
Each asset should include ownership, markets, valid uses, known variants, and the person authorised to make an enforcement decision.
2. Collect weak signals
Threat detection should combine automated monitoring with human observation.
Useful inputs include image matching, keyword monitoring, price outliers, marketplace reports, customer complaints, distributor feedback, social listening, warranty anomalies, and tips from authorities or industry associations.
The goal is not to capture every mention. It is to identify behaviour that creates a credible risk of deception, diversion, or harm.
3. Resolve identities and relationships
Individual alerts should be grouped into cases and networks. Teams can compare contact information, creative assets, catalogue structure, payment paths, shipping origins, and timing.
Identity resolution reduces duplicated work. It also helps the brand identify whether ten suspicious listings represent ten minor sellers or one coordinated operation.
4. Prioritise by commercial harm
Not every infringement deserves the same response.
Priority should reflect:
- customer safety risk;
- scale and velocity of exposure;
- likelihood of customer confusion;
- strategic importance of the product or market;
- damage to authorised partners;
- evidence quality;
- repeat behaviour;
- potential loss of data, payment, or identity.
A small account selling a dangerous counterfeit may deserve faster action than a large account using an outdated logo without commercial deception.
This risk-based approach extends [buyer-risk compression](/blog/marketing-needs-buyer-risk-compression). Brand protection should first address the threats that most increase uncertainty and potential loss for the buyer.
5. Orchestrate the response
The response may involve platform takedowns, cease-and-desist notices, distributor action, payment-provider alerts, customs coordination, law-enforcement referrals, customer warnings, or litigation.
The important capability is orchestration. Legal, brand, commerce, security, customer service, and market teams need a common case record and clear decision rights.
Without orchestration, one team removes a listing while another continues sending traffic to the same ecosystem.
6. Learn from recurrence
Closure is not the same as disappearance.
After action, teams should monitor whether the actor returns, which channels replace the original one, which product cues were copied, and which customer segments remained exposed.
Repeated infringement may reveal weaknesses in packaging, authorised-seller visibility, search ownership, channel governance, or customer education. Enforcement evidence should therefore improve the wider brand system.
Customer service is an intelligence sensor
Brand protection is often treated as a legal responsibility. That leaves valuable operational evidence unused.
Customer service sees patterns that monitoring tools may miss:
- customers asking whether a seller is authorised;
- warranty claims for products absent from official records;
- unusual complaints about quality or packaging;
- payment disputes linked to impersonated pages;
- confusion between official and copied accounts;
- reports of scams using brand executives or employees.
These signals should enter the same case system as platform and legal evidence.
The brand can also reduce harm by making verification easier. Official seller directories, serial verification, clear channel policies, consistent account naming, and visible reporting routes help customers distinguish authentic offers before purchase.
This turns protection into a customer-experience capability.
Evidence must be portable
Digital cases often move across organisational and jurisdictional boundaries. A platform, regulator, payment provider, distributor, or court may require different formats.
The evidence package should preserve:
- timestamps and source URLs;
- screenshots and original media;
- seller and transaction identifiers;
- relationship to the protected asset;
- evidence of customer confusion or harm;
- previous actions and repeat incidents;
- chain of custody and case ownership.
This follows the principle behind [brand evidence portability](/blog/brands-need-evidence-portability). Evidence creates more strategic value when it can travel credibly to the next decision-maker.
Measure reduced exposure, not takedown volume
High takedown numbers can indicate effective enforcement. They can also indicate that the same threat keeps returning.
Better measures include:
- time from detection to validated case;
- time from validation to action;
- customer exposure before removal;
- percentage of repeat offenders linked across channels;
- recurrence rate after action;
- share of high-risk cases with complete evidence;
- reduction in counterfeit complaints and warranty leakage;
- authorised-seller visibility in priority searches;
- customer success in verifying official channels;
- disruption of networks rather than individual listings.
The objective is not to produce a larger enforcement report. It is to reduce the commercial space in which deception can operate.
Governance matters before a crisis
Teams should decide in advance:
- who owns monitoring;
- who validates a suspected violation;
- what risk threshold triggers immediate action;
- who can communicate publicly;
- when regulators or law enforcement should be involved;
- how customer remediation will occur;
- how evidence is retained;
- how lessons change product, channel, and campaign decisions.
These rules reduce delay when a high-velocity incident emerges.
They also protect against overreaction. Not every critical review, reseller, comparative claim, or fan account is an infringement. Mature protection distinguishes legitimate expression from deceptive commercial behaviour.
Conclusion
Registration gives a brand enforceable rights. Threat intelligence turns those rights into operational protection.
Digital infringement moves across accounts, platforms, content, payments, and fulfilment networks. Brands must therefore detect patterns, prioritise harm, preserve portable evidence, coordinate action, and learn from recurrence.
The strongest protection system is not the one that files the most takedowns. It is the one that shortens customer exposure, disrupts repeat networks, and makes authentic commerce easier to recognise.
In digital markets, ownership is legal. Protection is operational.
Key Takeaways
- Trademark registration is necessary but insufficient for digital brand protection.
- Online infringement should be analysed as a connected network, not isolated listings.
- Cases should be prioritised by customer and commercial harm.
- Customer service, authorised partners, and commerce teams are important intelligence sources.
- Success should be measured through reduced exposure and recurrence, not takedown volume alone.
FAQ
What is digital brand threat intelligence?
It is the continuous process of detecting, connecting, prioritising, and acting on signals of impersonation, counterfeiting, deception, and intellectual-property misuse across digital channels.
Is trademark registration still important?
Yes. Registration establishes the legal basis for enforcement, while threat intelligence helps the organisation detect and respond to violations in practice.
What should brands monitor?
They should monitor suspicious sellers, copied creative assets, pricing anomalies, domains, advertisements, social accounts, customer complaints, payment paths, and recurring fulfilment patterns.
How should brand-protection performance be measured?
Measure detection speed, exposure duration, evidence quality, recurrence, network disruption, customer harm, and the visibility of authentic channels.